/PRNewswire/ -- exida, a global pioneer in industrial automation and control system (IACS) cybersecurity and the world's first accredited IACS Certification...
European Systemic Resilience: Sovereign Capabilities - Critical Infrastructure and the Architecture of National Continuity - Economy https://debuglies.com
EU Machinery Regulation applies from January 2027 and the Cyber Resilience Act from late 2027, with
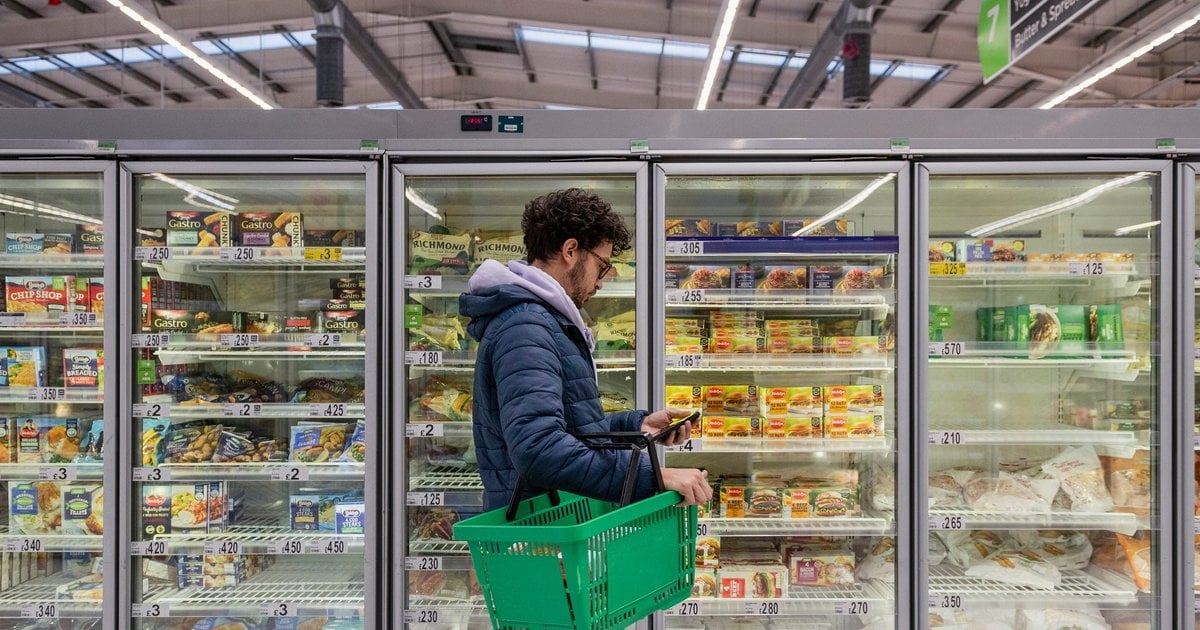
In this Cyber Magazine Reacts feature, cyber experts respond to the large-scale cyberattack affecting supermarket freezers across seven countries in Europe

The EU CRA, mandatory in Dec. 2027, requires connected devices to build security into flash memory, protecting identity, data and updates.

Macronix integrates cryptographic authentication, secure boot and tamper protection into flash memory to strengthen connected-device security.
Three weeks after French supermarkets were targeted, more remote cyberattacks forced grocers in Belgium and Sweden to dump spoiled inventory, proving that operational cold-chain hacks are now a repeating industry threat.
Supermarket and grocery store refrigerators across Europe appear to have been hacked early Monday — the second such incident in recent weeks where attackers have manipulated temperature controls and caused stock to spoil.
The EU Cyber Resilience Act faces questions over its economic impact as third-party estimates point to substantial compliance costs, competitive pressures and unresolved concerns about whether its requirements meet established proportionality and competition norms.
Here, Callie Reis, VP Industrial Automation Advisory Services at Schneider Electric, explains why early data AI-enabled visibility and industrial intelligenc...
A recent warning from the Five Eyes intelligence security agencies states that AI-powered cyber incidents are anticipated to 'fundamentally transform offensive and defensive cyber capabilities'.
Rockwell's SecureOT helps OEMs meet EU cyber rules with assessments, compliance reports and monitori

Your suppliers now have 24 hours to tell you. Do you know what you are running? writes Dan Jones, Senior Security Advisor, EMEA at the cyber platform Tanium. T

With Regulation (EU) 2024/2847 – better known as the Cyber Resilience Act, or simply the CRA – the European Union is introducing a horizontal cybersecurity framework for products containing digital elements.
UK software liability entered the government’s formal agenda on October 28, 2026, when Chancellor John Healey’s Autumn Budget pledged a consultation on making software vendors responsible for cyber breaches -- a first for any British administration, timed as the EU enforces fines of up to 15

The EU Cyber Resilience Act now applies to chip and IP suppliers, with reporting obligations active since September 2026 and full conformity requirements, including CE marking, arriving December 11, 2027. Learn about scope, documentation and readiness tools.

Determining which products may fall within the CRA's scope and what information may need to be provided to customers.
Expanding regulatory regimes in the U.S. and EU, including NIS 2, DORA, CRA, amended Regulation S-P and SEC rules, are compelling organizations to reassess their approach to handling the first 72 hours of a cyber incident. We analyze the actions companies should consider in light of the regulatory framework.
The EU Cyber Resilience Act (CRA) requires manufacturers to build cybersecurity features directly into products with digital elements before they enter the EU market. The CRA emphasizes secure-by-design principles and mandates ongoing security assessments and updates throughout a product’s lifecycle. …
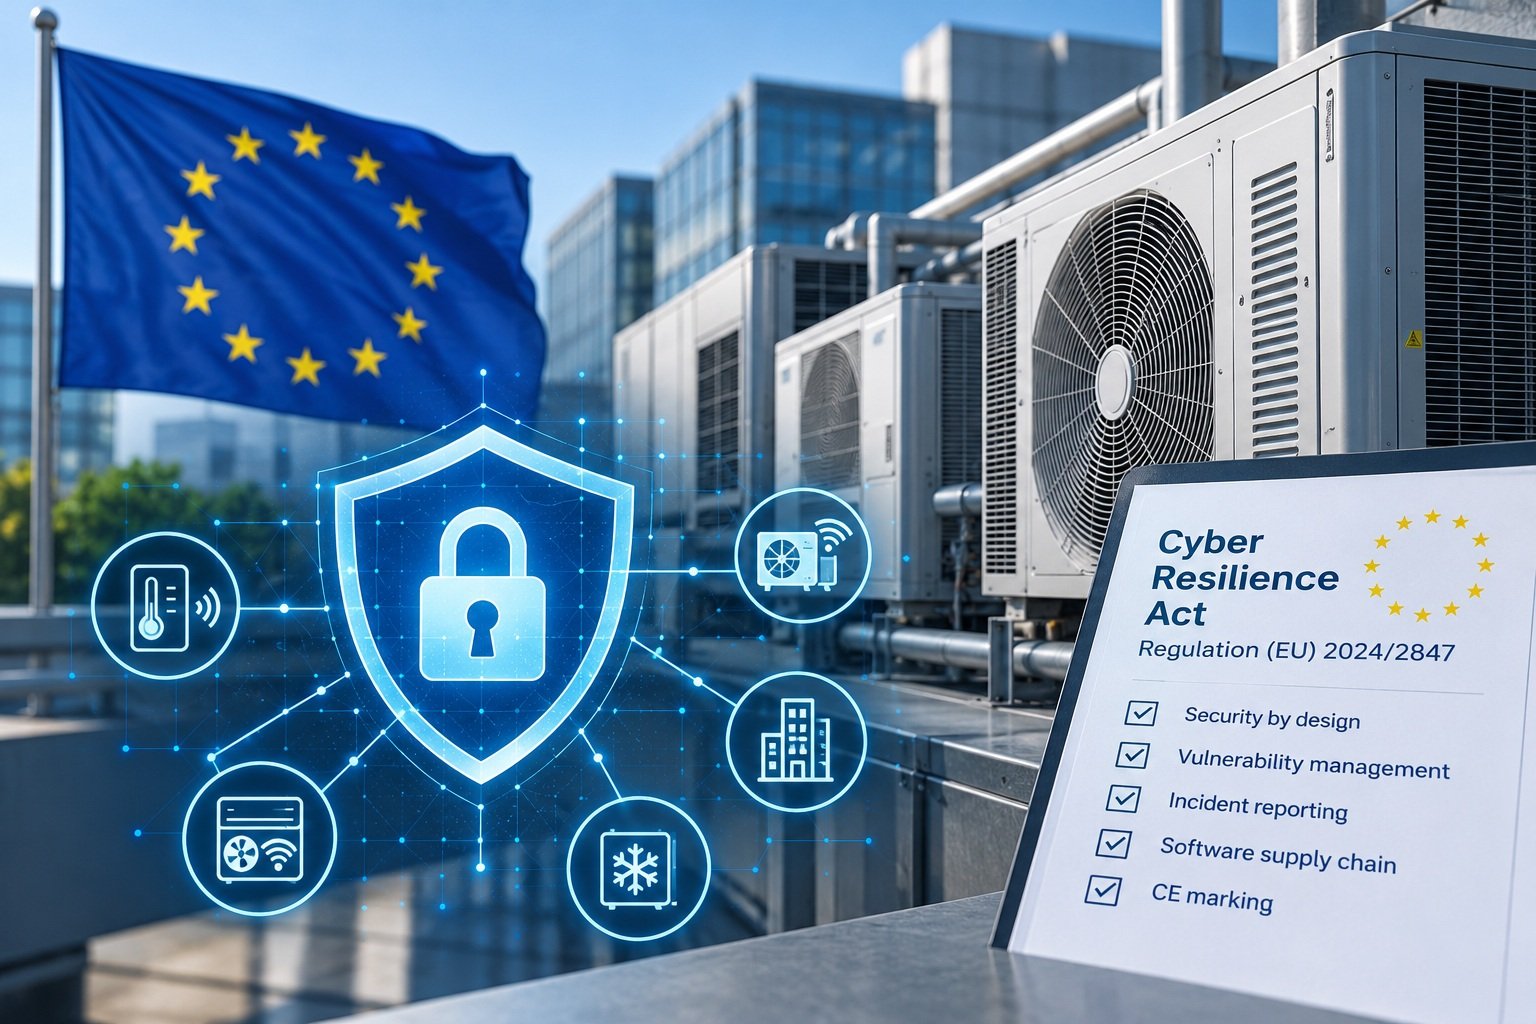
Manufacturers face new reporting duties and must prepare connected HVAC/R portfolios for full compliance by 11 December 2027.
From 11 September 2026, makers of digital products sold in the EU must report exploited vulnerabilit
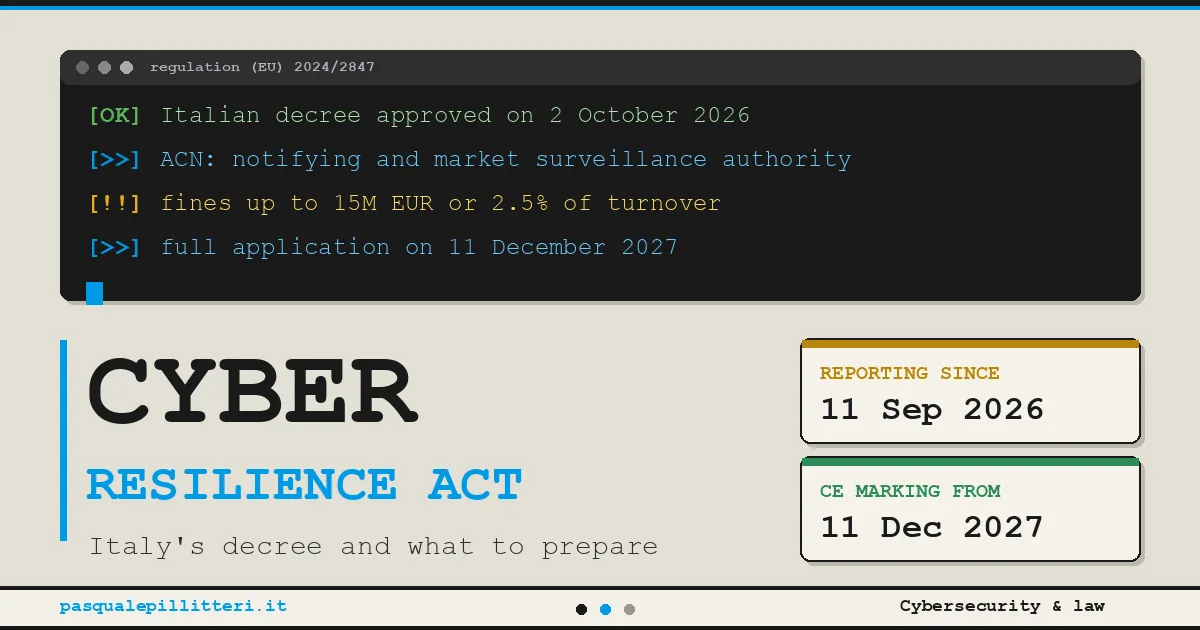
Italy's draft decree names the ACN as regulator and Germany's Bundestag has passed its law. What manufacturers must prepare before 11 December 2027.
Although the final versions of the EN 62443 standards have not been released, manufacturers can use existing standards to start preparing to comply with them.
ENISA is the EU agency dedicated to enhancing cybersecurity in Europe. They offer guidance, tools, and resources to safeguard citizens and businesses from cyber threats.

Agenzia per la Cybersicurezza Nazionale (ACN)'s Luca Nicoletti explains what the agency has built with millions of recovery money, what cyber resilience means beyond the box-ticking, and what Italy must settle to keep it all running.